A multisignature  Bitcoin market price and chart wallet requires more than one approved signature before certain funds can be spent. Instead of depending on a single key, a setup may require two signatures from three designated keys or three from five. This can reduce reliance on one device or person, but it introduces coordination and recovery requirements that simpler wallets do not have. The arrangement must be designed around the actual people and threats involved.
Bitcoin.org’s wallet-security guidance identifies multisignature as a way for groups or individuals to protect funds against compromise of a single device. The important distinction is that wallet rules specify a signing threshold; a mobile app displaying several user accounts is not necessarily enforcing a multisignature policy on-chain.
What a signing threshold means
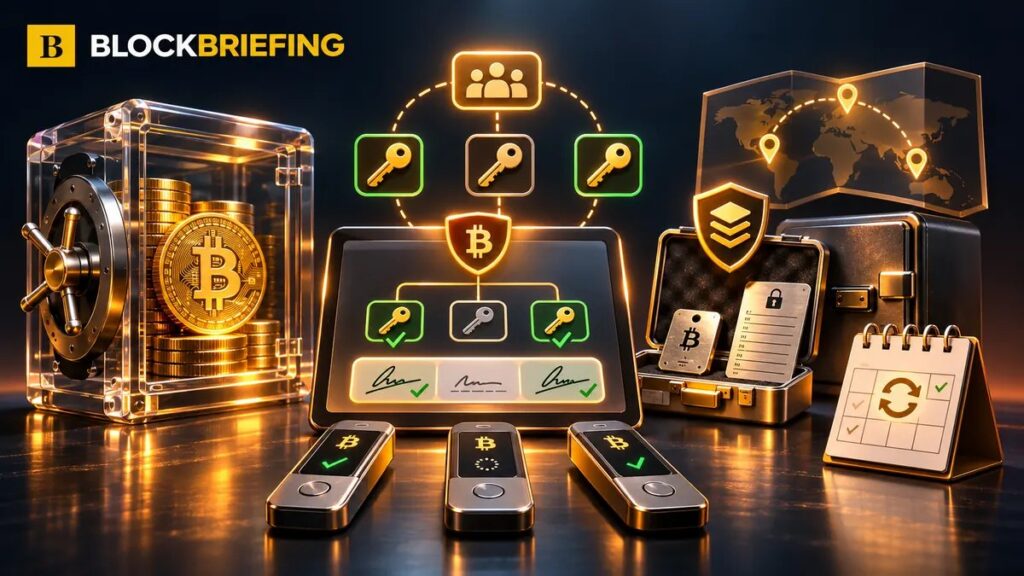
In a two-of-three arrangement, any two authorized keys must sign a valid spending transaction. Losing one key may not prevent access if the other two remain available. Conversely, an attacker who obtains only one key should not be able to move funds under the intended policy. This protection assumes the keys are genuinely independent and that the wallet’s configuration has not been replaced or misrepresented.
A three-of-five arrangement can distribute authority across a company treasury, partnership or family arrangement. It should not be confused with splitting one recovery phrase into five pieces without a documented reconstruction method. Multisignature keys are independently generated signing authorities, while secret-sharing systems involve different trust and recovery properties. Mixing the two concepts can create dangerous false confidence.
Why configuration backups matter
A multisignature wallet may need more than individual seed backups to reconstruct its addresses and spending policy. Depending on the wallet implementation, users may need the complete set of public keys, derivation information and wallet descriptor or configuration file. Without this data, independently backed-up keys may be insufficient to locate or correctly spend existing outputs.
Bitcoin Improvement Proposal BIP-45 describes one historical approach to deterministic multi-party wallets. It illustrates why standardized key derivation and shared public information matter for interoperability. It is not a guarantee that every modern multisignature wallet uses that exact specification. Wallet owners should follow the configuration export and recovery requirements of their actual software.
Distributing the keys
If every signing device and backup is kept in the same bag, theft or fire can defeat the purpose of multiple signatures. Separating key custody can reduce correlated losses but may make urgent transactions slower. For organizations, written approval procedures and clear signer replacement rules matter as much as the cryptography. A legitimate threshold transaction still can be a mistaken payment if all required signers approve a malicious destination.
Coordination creates trade-offs. A signer’s death, departure or unavailability may prevent a threshold from being met. Lost configuration files may complicate restoration, while a compromised coordinator application could present misleading transaction details. Testing with modest balances and performing periodic recovery drills can expose problems before they affect significant funds.
When multisignature is appropriate
Shared treasuries, long-term family custody and certain high-value savings arrangements can benefit from separate signers and locations. People making small, frequent payments may find the extra operational burden disproportionate. Any design should document signing thresholds, backup locations, emergency access, successor responsibilities and device verification. The best policy is one that can still be executed reliably after a realistic failure, not simply the policy with the most keys.
A practical two-of-three example
Imagine a household holding long-term Bitcoin with three independent signing devices. One device is stored at home, another in a secure second location and a third with a trusted designated participant. Any two can authorize a payment; possession of one key alone should not be enough. The family must decide who can coordinate a transaction, how the signers verify a legitimate request and what happens if one person becomes unavailable. The arrangement is only useful if enough authorized people can still recover their keys when needed.
Wallet descriptors and compatibility
A modern multisignature setup often depends on a descriptor or equivalent wallet record containing public-key information, derivation paths and the spending policy. This material is generally not the secret signing key, but losing it can make restoration difficult even when private-key backups survive. Some wallets support different output types or derivation conventions, and an imported set of seeds may generate different addresses unless the correct configuration is used. A recovery plan should record the wallet format and confirm independent software can reconstruct the intended addresses.
Signers should verify more than a transaction hash
In an organizational wallet, each participant should check the recipient, amount, network and transaction purpose independently. A malicious coordinator could ask honest signers to approve a transaction that benefits an attacker. The threshold mechanism confirms how many valid signatures were collected; it does not confirm that the payment was authorized under company policy. Dual-control payment reviews, spending limits, documented invoices and a pause for unusually large transfers address the human side of the threat.
Inheritance and organizational changes
A signer can die, depart a company, lose a device or become temporarily unreachable. The policy should specify successor access, the conditions for rotating signing keys and how the remaining authorized signers can transfer funds to a new wallet before the current threshold becomes unattainable. This is an operational and sometimes legal question, not merely a software feature. Avoid giving every participant all recovery phrases for convenience: doing so may collapse the supposed independence of the arrangement.
Costs and trade-offs
Multisignature transactions can consume different amounts of block space depending on script type and signing policy, affecting network fees. Setup and periodic testing also require time and careful documentation. Threshold schemes reduce certain single-key risks but can increase the risk of coordinated loss, inaccessible backups and confusion between signers. Some users may be better served by a simpler wallet with a strong backup plan. Before moving significant funds, conduct a realistic restoration exercise with a small amount and confirm that the policy works without the original coordinator.