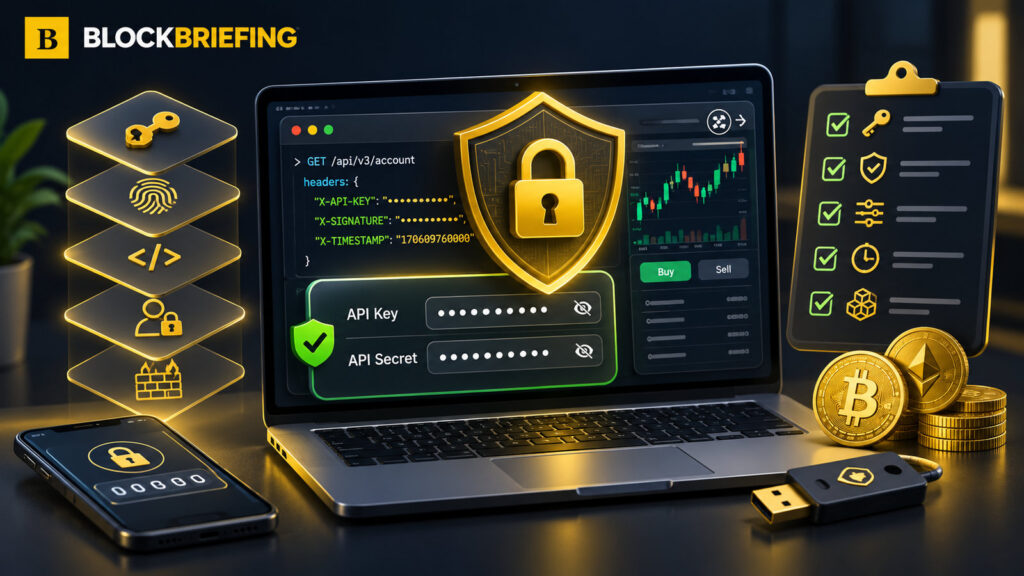
Crypto exchange API keys can let automated tools access account data, place orders and, where specifically permitted, transfer funds. The safest configuration gives each application only the permissions it needs, restricts where the key can be used and makes revocation straightforward.
The distinction between read-only, trading and transfer rights is essential. Coinbase Exchange’s official permission list demonstrates that these are separate access levels; users should confirm the actual options offered by their own platform rather than assume the same settings exist everywhere.
This guide explains how to set up, monitor, rotate and revoke exchange API credentials, including the different financial risks created by trading access and withdrawal access.
What Is a Crypto Exchange API Key?
A crypto exchange API key is a credential that allows software to interact with an account through an application programming interface. Instead of signing in through the usual website for every action, a trading application can use credentials to request data, post orders or perform other activities the user has authorized.
The key is not the same as a blockchain private key. A blockchain private key can authorize transactions from an on-chain wallet; an exchange API credential authorizes actions against a platform’s account system. Depending on permissions, the economic consequences of compromise may still be severe.
API access is useful for portfolio trackers, market-making software, tax reporting systems and automated trading tools. The security question is whether each tool receives only the access it genuinely needs.
Can Someone Withdraw Crypto Using an API Key?
Sometimes. The answer depends on the platform, the API product and the permission granted. Some exchange APIs support withdrawal or transfer permissions; other keys are limited to viewing balances or trading. Users should never assume all API credentials are read-only or, conversely, that every key permits funds to leave an account.
For example, Coinbase Exchange’s documentation distinguishes View, Trade, Transfer and Manage permissions. It describes Transfer as capable of moving value, including deposits and withdrawals, and notes the associated authorization implications.
A portfolio dashboard that only reads balances should not need trading or transfer privileges. A bot that places orders may require trading rights, but often has no legitimate reason to receive transfer permissions. Confirm those distinctions in the specific exchange interface before approving access.
The Four Types of Access to Understand
Read or View: software may retrieve account positions, balances, orders or history. Read access can expose sensitive financial information even if it cannot directly move funds.
Trade: software may submit, modify or cancel market orders. A compromised trading key can create expensive positions or unfavorable trades without having withdrawal access. Liquidity, slippage, margin requirements and liquidation risk can turn misuse into substantial financial loss.
Transfer or Withdraw: where supported, the key may initiate movement of funds. This capability deserves the highest scrutiny and should remain disabled unless a clearly documented business process requires it.
Manage or Administration: some APIs can modify settings, account lists or other parameters. Managing user settings may create indirect risks that are not obvious from a simple summary of permissions.
Apply Least Privilege From the Start
Least privilege means granting the smallest set of capabilities required to perform a task. Separate tracking, trading and operational integrations into different keys instead of using one all-powerful credential.
If a tax-reporting service needs historical trade data, authorize read access. If an automated strategy places orders but never transfers collateral to an external account, exclude withdrawal permissions. If a vendor requests broader access than its task requires, ask why and seek a narrower alternative.
The objective is not merely to prevent an attacker from accessing a secret. It is to limit the damage if any single service, computer or employee account is compromised. Multiple narrow keys also simplify incident response because each can be revoked without necessarily interrupting unrelated systems.
Use IP Allowlisting Where Available
An IP allowlist restricts credential use to specified network addresses. If an attacker steals a key but cannot send API requests from an approved address, the additional restriction can help prevent misuse.
Coinbase’s Exchange key setup guide identifies an IP allowlist as a required field for that API product. Other services may make it optional or implement it differently.
Allowlisting is not a replacement for keeping secrets secure. Cloud servers can be misconfigured, trusted addresses can be compromised and some applications operate from changing network locations. Users should verify that approved addresses belong to the intended service and review them when switching providers.
When the application runs from a personal device with a frequently changing internet address, use a supported secure infrastructure design rather than disabling every other safeguard simply to avoid connectivity problems.
Store Credentials as Secrets, Not Documents
A common mistake is to paste an API secret into email, a chat conversation, a public repository or a spreadsheet shared with collaborators. Treat an exchange API secret as a password with potentially greater financial consequences.
For self-operated software, store secrets in a reputable secrets manager or protected environment configuration rather than in source code. Limit read access to the applications and personnel that truly need the values. Never include a secret in a screenshot, support ticket or diagnostic log.
Create separate keys for production and testing systems. Avoid copying a live trading key into a development laptop or test environment; a bug or malware infection there can expose the production account.
If a secret was accidentally published, assume it may have been copied, revoke it and create a new credential. Merely deleting a public commit does not guarantee that the old secret has disappeared from all caches or clones.
Enable Strong Account-Level Security
API protection starts with the exchange account itself. Use phishing-resistant multi-factor authentication where available, unique passwords and an email account secured to the same standard.
Review account recovery methods, device sessions, authorized applications and withdrawal-address controls. On some exchanges, address allowlisting restricts transfers to a set of approved destinations. This provides a separate defense against unwanted withdrawals, subject to the platform’s specific implementation.
It is important to distinguish exchange API keys from approvals made through a decentralized wallet. A wallet token allowance is an on-chain permission given to a smart contract; revoking an exchange API key does not necessarily revoke a contract allowance. The procedures are different.
For wallet approvals, consult the underlying wallet provider’s guidance, such as Coinbase Wallet’s documentation on token approvals.
Monitor Orders and Audit Logs
A compromised key does not have to withdraw funds to cause damage. Unauthorized orders can shift exposure, incur fees or interact with illiquid markets. Monitoring should therefore include positions, newly created orders, canceled orders and changes to leverage or margin.
Review API activity logs for unknown source addresses, unexpected times and changes in behavior. Establish alerts for new keys, privilege changes and attempts to transfer funds. Some platforms expose richer audit data than others; confirm which signals are actually available.
Teams should document who owns an integration, what it is supposed to do and who can stop it. Having a known emergency contact and a clear revocation procedure reduces confusion during a live incident.
A sudden unexplained trade is not proof of API compromise; software bugs, authorized strategies and manual trading can produce similar symptoms. Preserve logs and transaction records when investigating.
How to Revoke or Rotate an API Key Safely
Sign in through the exchange’s official website or application, navigate to API management, identify the integration and remove or revoke the old credential. Do not follow login links from unsolicited messages claiming that your account has been compromised.
Coinbase’s rotation instructions describe revocation, replacement, minimal permissions, allowlisting and testing. Exact menus and timing differ across providers.
If a compromised key is suspected, revocation comes before creating a replacement. Check whether disabling a key also stops automated liquidation protection or order-cancellation logic. Arrange alternative risk monitoring and examine orders already submitted to the exchange.
Test the replacement with a limited operation before restoring full automation. Log the date of rotation, the integration owner and permissions. Use a regular review schedule, but treat suspected exposure as a reason for immediate action.
What to Do After a Third-Party Security Alert
First, independently verify the alert from the exchange or vendor’s authenticated official channels. Then determine which keys were granted to the affected service. Revoke exposed or suspect keys and review activity for the entire plausible exposure window.
Next, inspect open orders, derivatives positions, collateral movements, withdrawal requests and recent account logins. Change passwords if broader account access is suspected and review authorized devices. Where suspicious trading occurred, preserve detailed records and contact the exchange through official support.
Do not reconnect automatically when the vendor merely posts a short reassurance. Look for a documented remediation and, where appropriate, confirmation from the exchange that integration access can safely resume.
The November 2026 SignalPlus API-key incident illustrates why exchanges can revoke integrations proactively even when they report their own systems were unaffected.
Third-Party Bot Due Diligence
Before granting credentials, identify the provider’s legal entity, supported exchanges, required permissions, data retention practices, incident disclosure procedures and how it stores customer secrets.
A claim that an integration is safe because it cannot withdraw funds ignores trading-related attack paths. Ask whether an attacker could create leveraged positions, trade illiquid markets, alter strategy settings or cause an order cascade.
Prefer providers that allow separate API accounts, clear revocation instructions and written statements of their permission needs. Security audits can be informative but do not guarantee that a deployed system is free of vulnerabilities.
A well-managed integration should also function correctly when permission is removed. Dependence on a vendor should not prevent the account owner from managing risk directly through the exchange.
Practical API Security Checklist
Before connection: confirm the domain, enable account MFA, create a dedicated key, disable unnecessary permissions and restrict approved IP addresses where supported.
During operation: monitor recent orders and account activity; avoid sharing secrets in code or chat; maintain records of which tools hold access; and remove unused integrations promptly.
During incident response: revoke suspect keys, verify positions, collect logs, review any transfers and consult official support. Afterward, only restore access using new credentials and documented permissions.
For readers managing assets outside centralized platforms, see BlockBriefing’s editorial verification resources and related wallet-security explainers. This guide is educational and cannot replace platform-specific security documentation or professional incident response.